 AgentNod
 for Codex
Codex approvals, next to everything else
When Codex wants to run a command, AgentNod shows the request as a card with the full command and a risk label. Your answer goes back to Codex through its hook, and the agent carries on.
Join the beta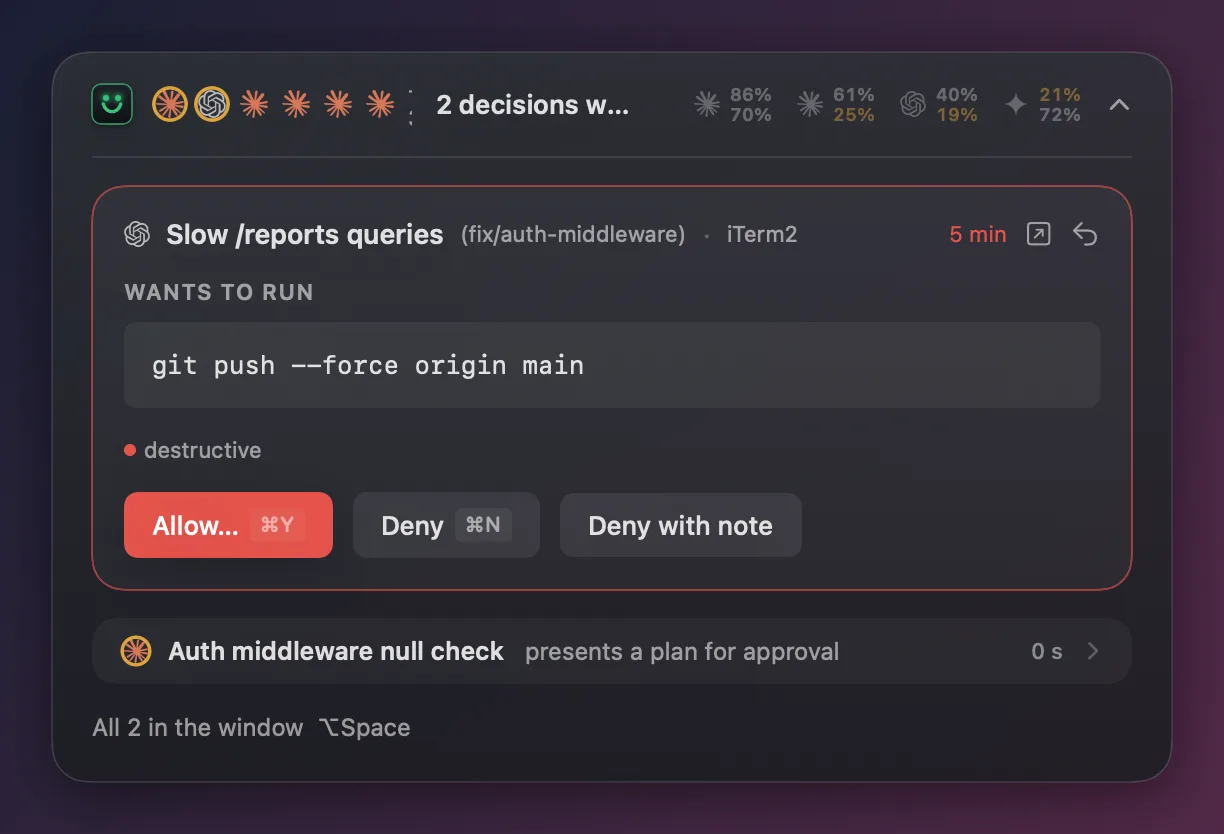
What you see
Codex requests land in the same queue as Claude Code and Cursor, oldest first. Each card names the session, its folder and branch, the terminal it runs in, and how long it has waited.
A destructive command such as a force push turns the card red, and Allow asks a second time.
How you answer
Allow, Deny, or Deny with a note. Codex receives the note as the reason for the denial, so a line like "use pnpm" changes what it tries next.
The arrow on the card hands the prompt back to the terminal.
Setup
Install writes AgentNod's handler to ~/.codex/hooks.json. Codex runs a user-level hook only once it is trusted, so AgentNod also writes the matching trust entry to ~/.codex/config.toml and leaves the rest of that file as it is. hooks.json gets a .before-nod copy first.
AgentNod reads Codex's usage from Codex's own session log, so the menu bar shows what is left in your Codex limits without an API call.